Catalogue
Services with a bright legal line
Everything below is performed under written authorization against systems you own or control. If your brief requires someone else’s phone, mailbox, or wallet, we will decline it on the first call.
Core engagement
Penetration testing
We simulate a determined attacker against a defined target set — external perimeter, internal network, or both — and deliver findings your engineers can actually ship against. Every test starts with written authorization and a Rules of Engagement.
View the engagement →
Adversary simulation
Red team operations
Red team work answers a different question than a pentest: would your people, process, and tooling notice a patient adversary? We run assumed-breach and limited-scope campaigns against objectives you set — with a kill-switch and legal cover in place.
View the engagement →
Product security
Web application security
We review the application your customers use — not a generic OWASP checklist in isolation. Expect deep work on authorization, tenancy, payment flows, and API contracts, with tickets your developers can pick up.
View the engagement →
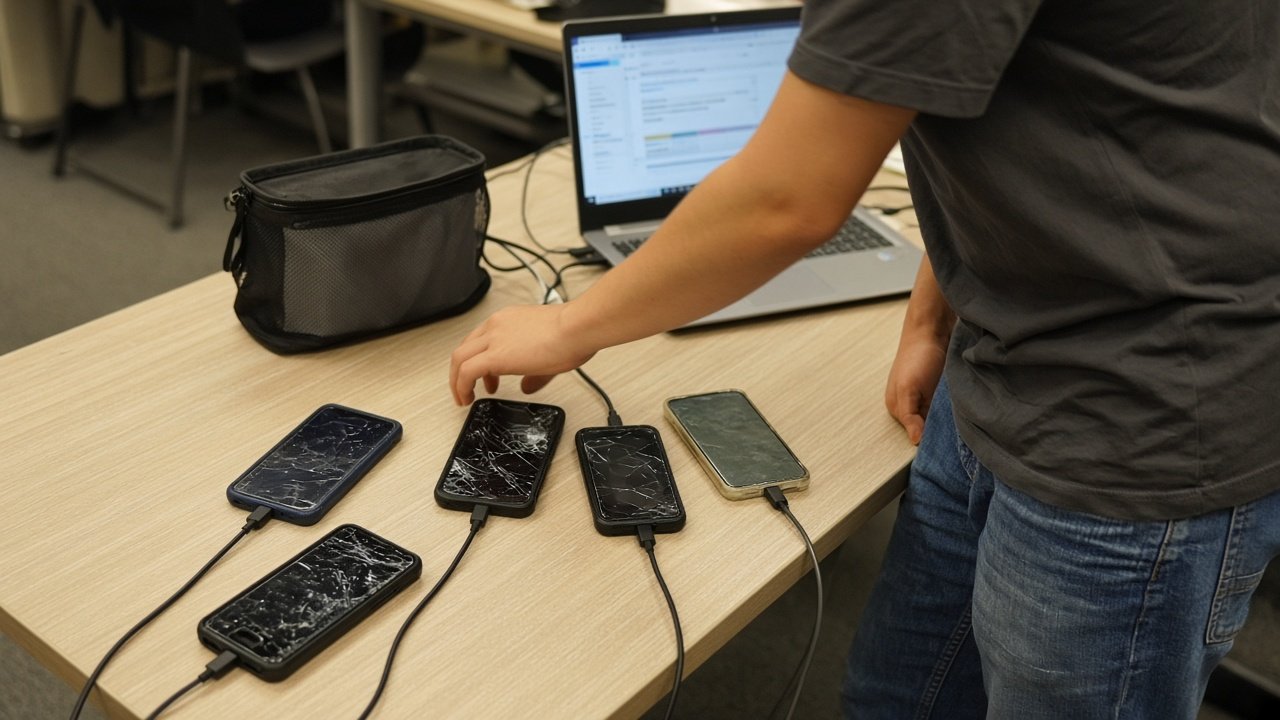
Your product, your devices
Mobile application security
We assess the mobile applications you ship — binary protections, local storage, certificate pinning, API backends, and jailbreak/root resistance. This is product security for your app. It is not access to anyone’s personal phone.
View the engagement →
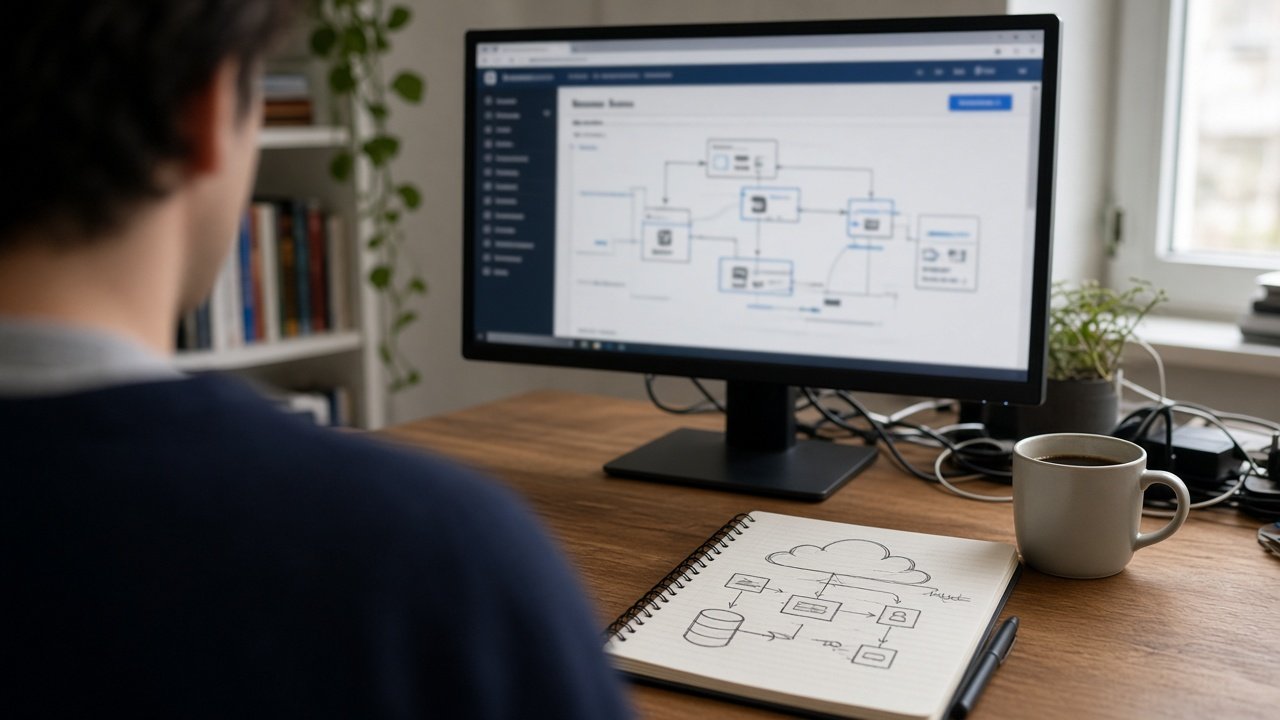
AWS · Azure · GCP
Cloud security assessment
Cloud reviews fail when they stay in CIS benchmark theatre. We map identity, network exposure, secrets, and workload paths in the subscriptions you authorize — then show what an attacker with a leaked key could reach.
View the engagement →
Breadth with judgement
Vulnerability assessment
When you need inventory and signal rather than a full adversarial test, we run authenticated scanning plus analyst review. Noise is stripped. What’s left is a ranked backlog with owners in mind.
View the engagement →
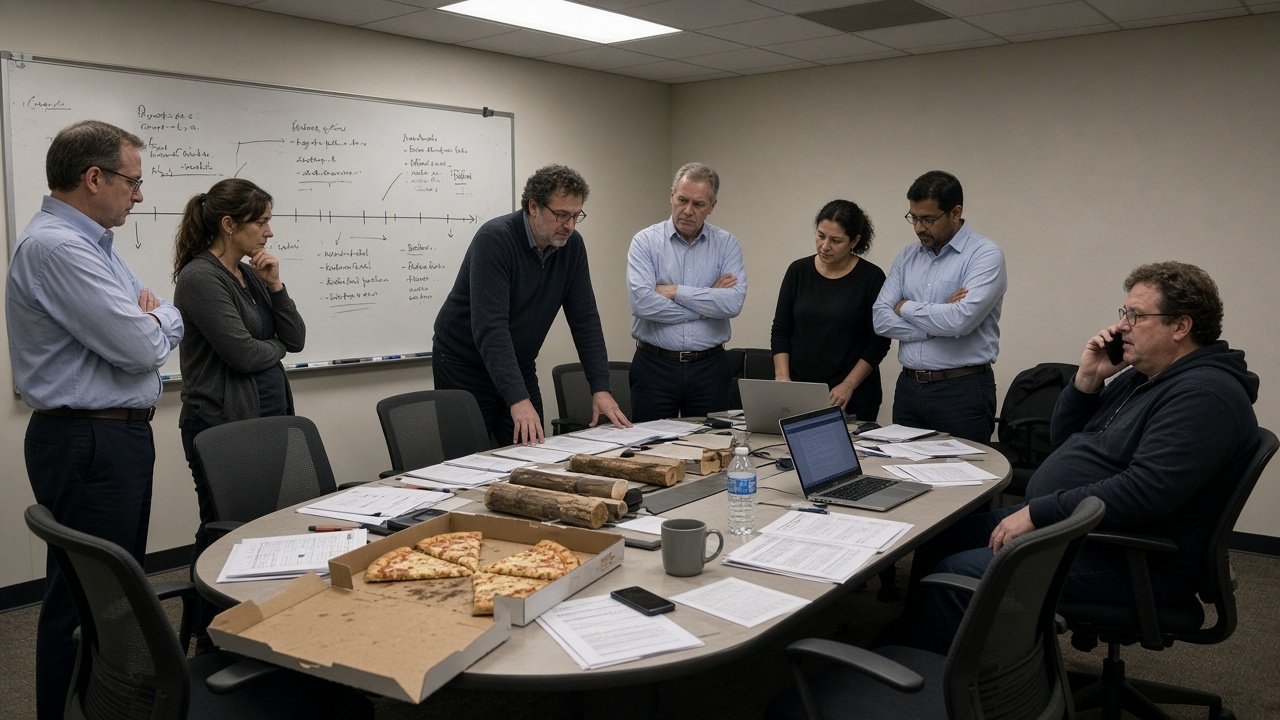
When something is already wrong
Incident response
Retainers and emergency response for organizations that have a confirmed or suspected incident. We preserve evidence, contain where instructed, and work alongside your counsel. We do not attack third parties, seize wallets, or ‘hack back’.
View the engagement →
People and process
Security awareness & tabletop
Phishing simulations, executive tabletops, and role-specific workshops designed around how your company actually works. The goal is better decisions under pressure — not humiliating anyone in Slack.
View the engagement →
Next step
Not sure which engagement?
Send the question you need answered. We will recommend a pentest, a scan, a red team, or a retainer — or tell you to wait a quarter.